

Outlook Add-in overview
Overview
Section titled “Overview”The Opensense Outlook Add-in is a centrally managed Microsoft 365 Integrated App that automatically applies your company’s email signatures to every email composed in Outlook, on desktop, web, and mobile. Your IT team deploys and manages it, and end users don’t need to do anything.
This article is for IT admins who configure or manage the add-in. It explains how the add-in works, the deployment methods and their tradeoffs, and links to all the articles in this section.
How it works
Section titled “How it works”Once deployed, the add-in loads automatically when a user opens a new compose window in Outlook, and inserts their assigned signature. How that signature is handled depends on your deployment method:
- Client-side
- The signature is sent directly with the email from Outlook.
- Server-side stamping
- The signature is cleared from the compose window before the email is sent, and Opensense's servers apply the signature during routing.
The add-in is deployed through Microsoft 365’s Centralized Deployment. Your admin assigns users or groups in the Microsoft 365 admin center, and the add-in installs silently across Outlook desktop, Outlook on the web (OWA), and Outlook Mobile.
Deployment methods
Section titled “Deployment methods”The add-in supports three deployment methods. The right choice depends on how much compose-window visibility your employees need, and how much server-side control your organization needs for compliance and marketing.
-
Server-side, after send
Stamping
Signatures are applied entirely server-side after send. Nothing is inserted into compose.
- The add-in pane shows a preview of what recipients will receive
-
Recommended
Plain Text Block
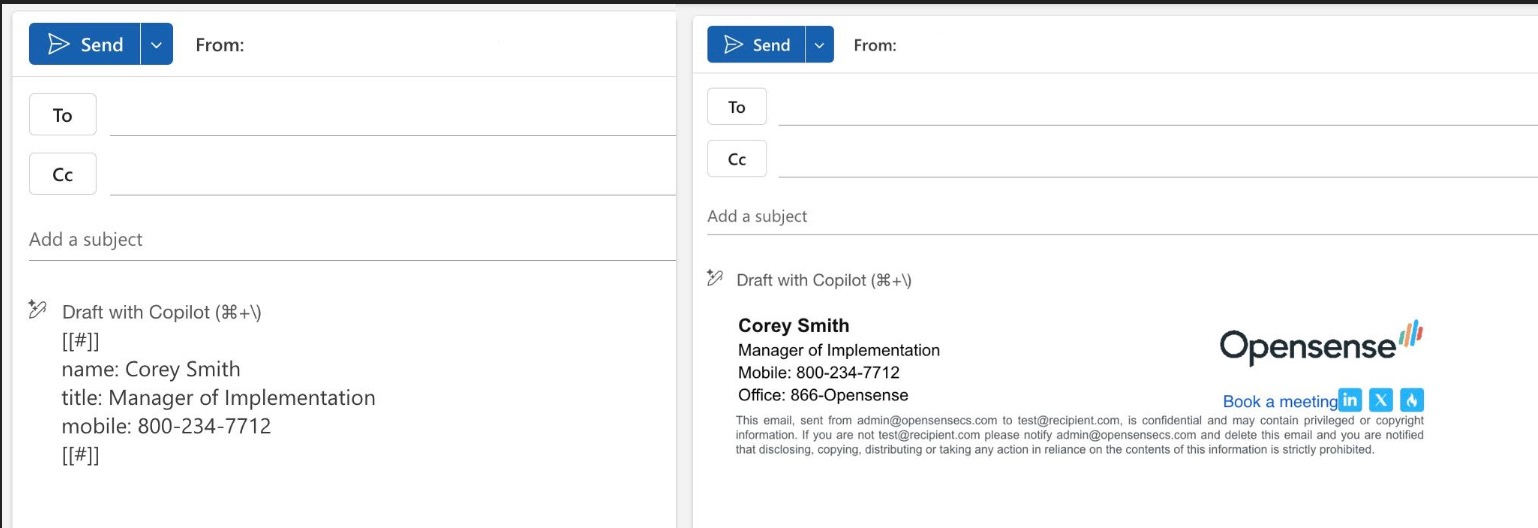
The add-in inserts a token into compose. A mail flow rule routes the email to Opensense for server-side transformation.
- The add-in pane shows a preview of what recipients will receive
- Opensense's patented approach, recommended for most deployments
-
Client-side, in compose
Visual Preview
The full HTML signature is rendered client-side in the compose window.
- Users can see and edit it before sending
Comparing the methods
Section titled “Comparing the methods”For each method’s strengths and limitations, and help choosing one, see Comparing Outlook Add-in deployment methods.
Server-side stamping with add-in signature removal
Section titled “Server-side stamping with add-in signature removal”The add-in removes any locally saved Outlook signatures before the email is sent. No signature is visible in the compose window. The email routes through Opensense’s servers after send, where the correct HTML signature and any marketing banners are applied before delivery.
Plain Text Block (patented)
Section titled “Plain Text Block (patented)”The add-in inserts a tokenized plain text block containing Opensense’s proprietary [[#]] trigger into the compose window, alongside a non-clickable visual preview of the final rendered signature. When the email is sent, a mail flow rule detects the [[#]] token and routes the message to Opensense, where it is transformed server-side into the full HTML signature before delivery.
Visual Preview
Section titled “Visual Preview”The add-in renders a live HTML signature directly inside the Outlook compose window. The signature is inserted client-side before the email is sent.
System requirements
Section titled “System requirements”The add-in needs Exchange Online, a supported Microsoft 365 or Office 365 license, and an Outlook client that meets the minimum version for Centralized Deployment. MSI-based installs and volume-licensed Office versions (Office 2016, 2019, and 2021) are not supported, because they don’t support the required API version.
For the full version table, platform support matrix, and unsupported environments, see Outlook Add-in supported environments.
Key deployment considerations
Section titled “Key deployment considerations”- Propagation time
- After a user or group is added to the add-in's deployment scope in Microsoft 365, it can take up to 72 hours for the add-in to appear in Outlook. Plan your rollout timeline for this, and add test users first to gauge propagation speed in your environment.
- Admin consent
- End users are prompted to accept permissions when the add-in deploys, unless an admin grants consent in advance. To avoid prompts that disrupt employees, grant admin consent in Azure Active Directory before launch. See Scoping Outlook Add-in users in the Microsoft 365 admin center.
- Nested groups are not supported
- Microsoft does not support nested groups for Centralized Deployment. Users must be directly assigned to a top-level Microsoft 365 group. If your group structure uses sub-groups, add the users to a top-level group manually.
- Third-party email platforms
- The add-in only applies signatures to emails composed in Microsoft Outlook. Emails sent through third-party platforms such as Outreach, Salesloft, or Salesforce are not covered. For those platforms, use Opensense's routed mail flow integrations.
- Outlook Mobile From switching
- On Outlook Mobile, the add-in passes only the primary account context to the API. If a user switches the From address to an alias or shared inbox, the add-in does not update the signature for the switched identity. This is a Microsoft platform limitation, and it applies to all deployment methods.
End user experience
Section titled “End user experience”For most employees, the add-in needs no setup or action. Once your IT admin deploys it, the signature appears automatically when you compose a new email in Outlook. The add-in replaces or removes locally saved Outlook signatures.
Depending on your organization’s configuration, you see one of these:
- A plain text block in the compose window, with a non-clickable preview of your formatted signature
- A fully rendered HTML signature in the compose window (Visual Preview)
- No visible signature in the compose window, with the signature applied automatically after send (Stamping)
To use the add-in on your mobile device, see Using the Opensense Outlook Add-in on iOS or Using the Opensense Outlook Add-in on Android.
Article directory
Section titled “Article directory”All Outlook Add-in documentation, by topic. If you’re setting up the add-in for the first time, start with Requirements and deployment.
Requirements and deployment
Section titled “Requirements and deployment”- Outlook Add-in supported environmentsMinimum version requirements, and supported and unsupported platforms.
- Scoping Outlook Add-in users in the Microsoft 365 admin centerDeploy the add-in and manage user scope in Microsoft 365.
Configuration
Section titled “Configuration”- Configuring the Outlook Add-in in Domain SettingsSignature insertion settings, alias and shared inbox behavior, editable fields, and inline images.
- Setting up multiple signatures in the Outlook Add-inTurn on and set up multiple signatures per user.
- Setting up Custom Compose Fields for the Outlook Add-inDropdown, checkbox, and free-text fields in the compose pane. Not compatible with Stamping.
- Expected behaviors in routed Outlook Add-in deploymentsEdge cases for Stamping with field edits, shared account permissions, domain switching, and manual manifest installation.
Visual Preview
Section titled “Visual Preview”GCC and GCC High environments
Section titled “GCC and GCC High environments”- Opensense Outlook Add-in integration with GCC High environmentsCustom manifest deployment, directory sync requirements, and mobile configuration for GCC High.
- Outlook mobile add-ins in GCC and GCC High environmentsTurn on mobile add-ins in GCC environments, where they are off by default.
Troubleshooting and offboarding
Section titled “Troubleshooting and offboarding”- Troubleshooting the Outlook Add-inMissing add-in, permission issues, signature not applying, cache clearing, and debugging.
- Removing the Outlook Add-in in the Microsoft 365 admin centerRemove users, or the add-in, from Microsoft 365.